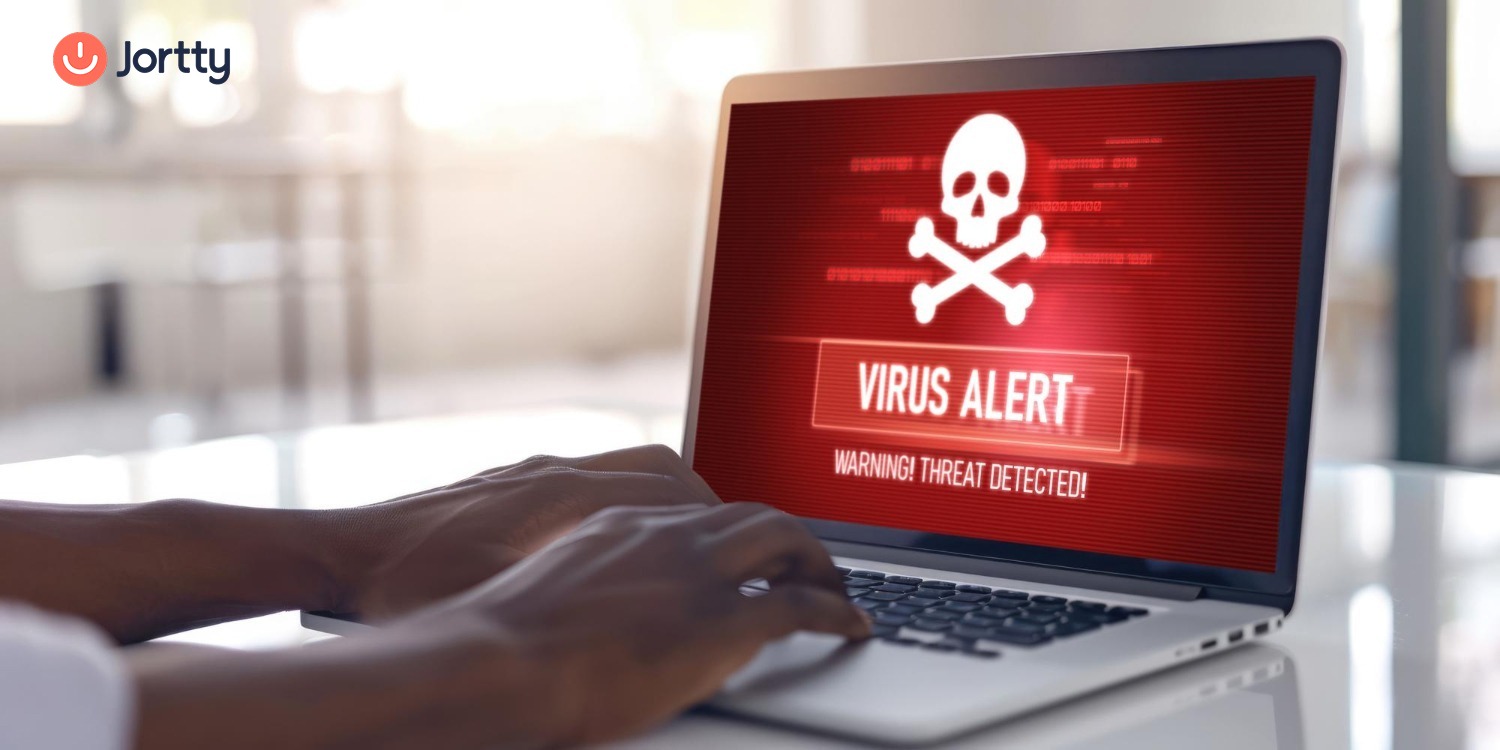
Computer viruses have been common since the earliest days of personal computing. However, today’s threats look nothing like the simple programs of decades past. Modern malware spreads faster, hides better, and often works alongside phishing and social engineering to cause real damage.
A clear idea of different types of threats out there doesn’t imply that you need to become a cybersecurity expert. It’s about spotting early warning signs and acting quickly, since many common threats can be reduced or prevented through basic security practices. With significant advancements in technology today, AI-powered scam detection can also help identify suspicious links, messages, and other social-engineering attempts that are often used to deliver malware.
At a Glance
- Viruses that infect files attach themselves to legitimate program files
- Ransomware locks files and demands payment for access
- Spyware quietly monitors activity without any user’s knowledge
- Trojans disguise themselves as safe, legitimate software
- Worms spread automatically across networks without any user action
Why These Threats Are Harder to Spot Than Before
Today, cyber threats hardly make themselves known the way traditional viruses did earlier with crashed systems or pop-ups. Most modern infections instead operate quietly in the background, making early detection challenging.
A couple of changes in how threats actually behave are:
- Malware avoids the obvious visible signs
- Threats bundle up with authentic-looking downloads
- Browser-based attacks mimicking real security warnings
- Infections that persist quietly for weeks
These silent techniques are common across browser scams, including fake certificate warnings designed to trick users into clicking something harmful. Understanding what a “Your Connection Is Not Private” warning means can help you avoid ignoring potentially important browser security alerts.
Recent data from CISA highlighted that the agency added 245 newly confirmed exploited risks in the past year. This brought the total number of tracked threats to 1,484.
The Threats Doing the Most Damage Right Now
Here are a couple of threats that account for the largest share of damage across both personal and business devices today.
File-Infecting Viruses
File-infecting viruses attach to legitimate executable files. They activate whenever an infected program runs. Once active, it spreads to other files on the same device. It is an old virus, yet one of the most damaging types.
How This Virus Spreads
- Gets attached to executable program files
- Automatically activates when the program runs
- Spreads to other files when in use
- Shared unknowingly through infected downloads
Timely software updates and avoiding downloads from unverified sources can notably reduce the likelihood of this type of infection.
Ransomware
Ransomware encrypts a victim’s files and demands payment to restore access. It often threatens permanent data loss if the deadline passes. It’s one of the most financially damaging threats that both individuals and businesses face today.
How Ransomware Typically Spreads:
- Phishing emails with malicious attachments
- Compromised remote desktop connections
- Infected software updates or downloads
- Exploited unpatched system risks
Regular backups that are stored separately from the primary system remain an effective defense. They reduce the pressure to pay when files are recoverable elsewhere. So, knowing how to detect and prevent phishing attacks matters, since a single clicked attachment remains the most common way ransomware gets its initial foothold.
Spyware
Spyware works silently in the background, monitoring a device’s activity. It often captures keystrokes, browsing habits, or login credentials without being detected. Unlike other disruptive threats, spyware is designed to remain hidden for as long as possible.
What Spyware Typically Targets:
- Keystrokes and typed login credentials
- Browsing history and personal habits
- Stored passwords and account details
- Depending on the malware, webcam or microphone activity
To stay protected, run regular security scans and review app permissions. This helps to catch spyware before it collects anything meaningful.
Worms
Worms are self-replicating programs that spread across networks without a user needing to click anything. Once inside one device, a worm can quickly move to every other connected system.
Why Worms Spread So Quickly:
- Exploit unpatched network vulnerabilities directly
- Require no action from the user
- Spread automatically across connected devices
- Often carry additional malicious payloads
Keeping operating systems and network-connected devices patched is one of the most effective ways to reduce the vulnerabilities worms exploit.
Trojan Horses
Trojans disguise themselves as legitimate software to trick users into installing them voluntarily. Once installed, they can open a backdoor for attackers, steal data, or download additional malware.
How Trojans Trick Users:
- Disguised as free or pirated software
- Bundled with seemingly harmless downloads
- Delivered through fake system update prompts
- Hidden inside malicious email attachments
Sticking to official app stores and verified sources removes most opportunities Trojans rely on to trick users.
Infostealers
Infostealer malware is designed to collect sensitive information such as saved passwords, browser cookies, authentication tokens, cryptocurrency wallet data, and other credentials.
Staying Ahead of Threats That Keep Evolving
Cyber threats will keep evolving, and staying protected has less to do with recognizing every threat by name and more to do with building consistent habits around updates, backups, and cautious clicking. Most infections still rely on a moment of distraction rather than a technical breakthrough.
Jortty uses AI-powered scam detection to help identify suspicious messages, links, and other potential threats before they lead to costly mistakes. When something looks suspicious, users can also get guidance on what to do next.
Frequently Asked Questions
Can a computer get infected without downloading anything?
Yes. Some threats can exploit vulnerabilities in browsers, operating systems, or network services without requiring you to intentionally download a file. However, modern browsers and operating systems include protections that make these attacks more difficult, especially when they are kept updated.
How can I tell if my device is already infected?
Possible warning signs include unusual slowdowns, unexpected pop-ups, unfamiliar programs, unexplained network activity, or unusual battery drain. However, many infections show few or no obvious symptoms, so security scans and device monitoring are more reliable than symptoms alone.
Is antivirus software alone enough to stay protected?
Antivirus software helps significantly, but pairing it with cautious browsing habits, regular backups, and updated software offers much stronger protection.